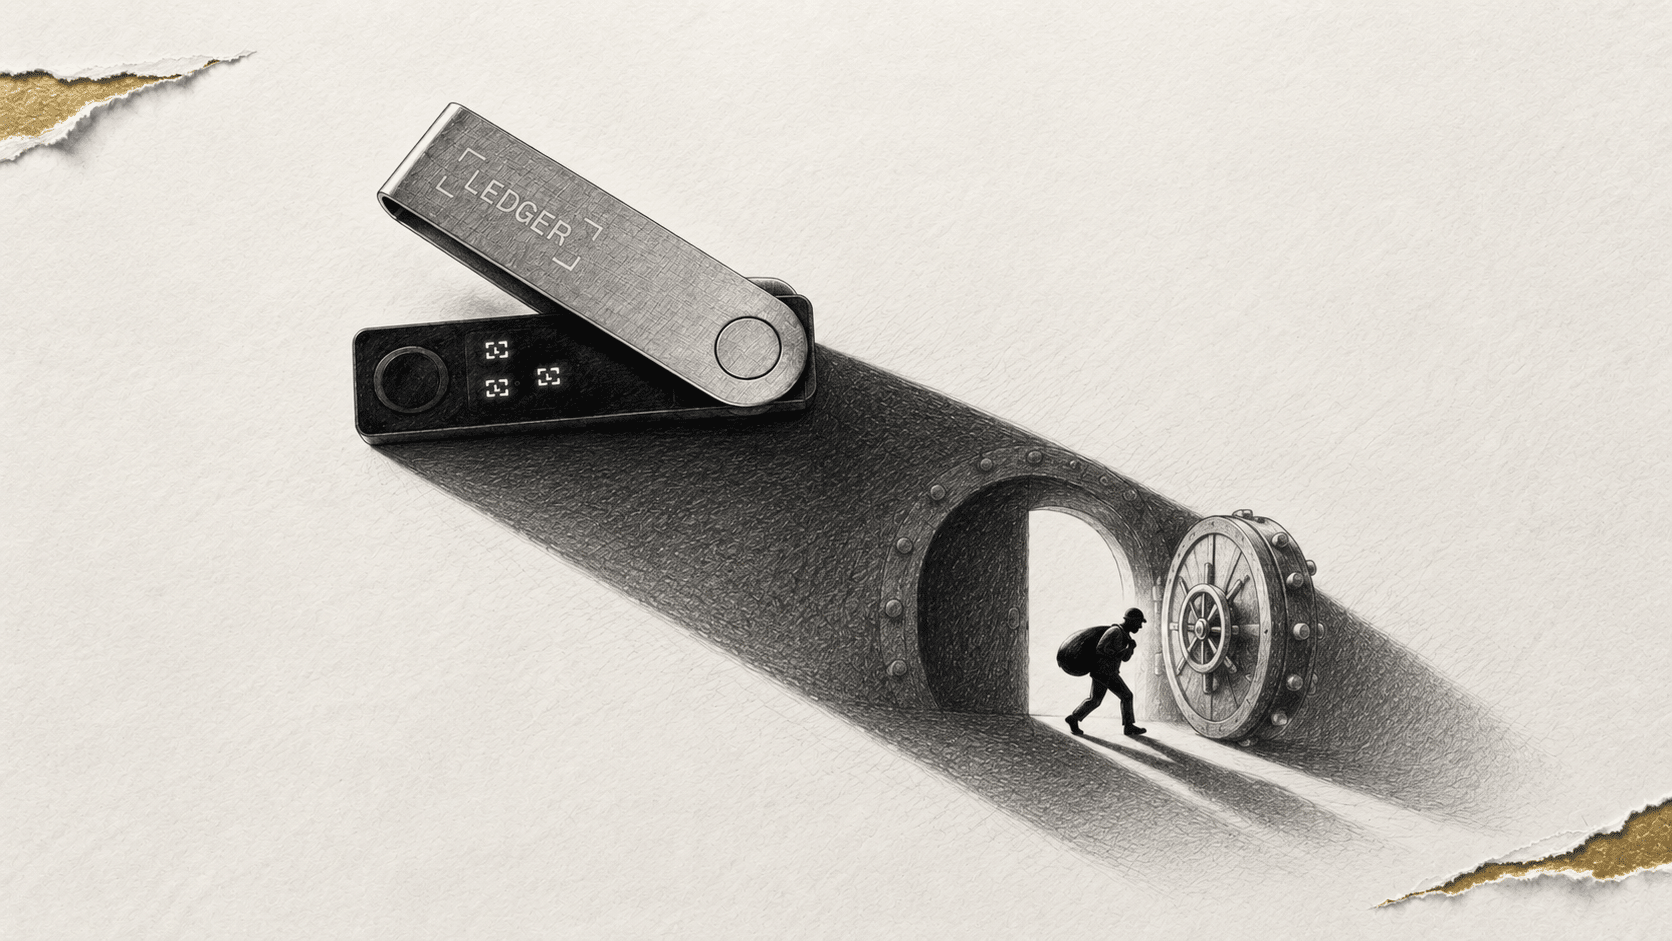
Ledger Says Unauthorized Component in CryptoBilis Wallets Leaked Recovery Phrases Over Cellular
By Unchained
AI summary of the source article
Ledger discovered an unauthorized hardware component in devices sold by reseller CryptoBilis that transmitted recovery phrases over cellular networks. All confirmed fund losses linked to the incident involve devices purchased through CryptoBilis.
Why it matters
Ledger CEO Pascal Gauthier highlighted that “Physical supply chain tampering is a risk for the whole industry.”
Key facts
- An unauthorized implant inside Ledger signers sold by reseller CryptoBilis decoded recovery phrases shown on the screen and transmitted them over LTE via a provisioned eSIM.
- Ledger confirmed that every verified fund loss tied to the incident involved devices sold through CryptoBilis, which has ceased selling Ledger devices.
- The implant did not modify the Secure Element or Ledger operating system, and Ledger reported no indication that its infrastructure or systems were compromised.
Source excerpt · Unchained
Ledger said the add-on part, found in devices from a Southeast Asian reseller, left its Secure Element and operating system untouched, and that every confirmed drain so far involves a CryptoBilis-sold signer. The post Ledger Says Unauthorized Component in CryptoBilis Wallets Leaked Recovery Phrases Over Cellular appeared first on Unchained .